PHP2Shell on CentOS 6: Patched PHP 5.3, 7.0 and 7.1
PHP2Shell (CVE-2026-109618, CVE-2026-109619) has no distribution or upstream fix on CentOS 6. Here is the in-place fix for the stock PHP 5.3 and Remi…
Practical guides to performance, security and life beyond end of support.
PHP2Shell (CVE-2026-109618, CVE-2026-109619) has no distribution or upstream fix on CentOS 6. Here is the in-place fix for the stock PHP 5.3 and Remi…
CVE-2026-98432 is a remote Linux kernel use-after-free. CentOS 7's stock kernel is not affected; ELRepo's kernel-lt and kernel-ml are and get no fix. The…
Cubic collapsed to 20 KB/s on a lossy long-haul path. BBR on the sender made it up to 50x faster, and a relay around…
PHP 8.2 reaches end of life on December 31, 2026: no more upstream security releases. Upgrade paths for current distros, and patched 8.2 packages…
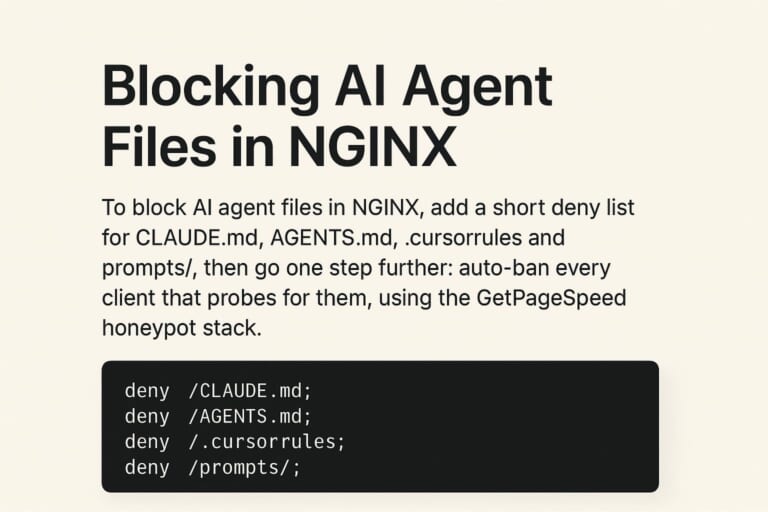
AI coding agents leave CLAUDE.md, AGENTS.md and prompt files in your web root. Block them in NGINX and auto-ban the scanners that probe for…
Can NGINX mitigate PHP2Shell (CVE-2026-109618, CVE-2026-109619)? Partly. Tested configs for blocking multipart and filtering uploads with ModSecurity, and why only patched PHP fixes it.
PHP2Shell (CVE-2026-109618, CVE-2026-109619) has no AWS fix for PHP 7.2 or 7.4 on Amazon Linux 2. Upgrade Amazon's php7.2 or Remi's php74 in place…
Install PHP 8.5 on CentOS 7 using base packages or a parallel collection, with PHP-FPM, built-in OPcache and clear extension compatibility guidance.
PHP2Shell (CVE-2026-109618, CVE-2026-109619) is a critical unauthenticated PHP RCE. Fixes for Ubuntu 20.04/18.04 and Debian 10 are Ubuntu Pro or ELTS only, and sury…
GetPageSpeed Amplify now has a hosted MCP server. Connect Claude Code, Cursor, VS Code or Codex and ask about NGINX CVEs, gixy config findings,…
Free tools to validate, troubleshoot and improve your infrastructure.
Validate and troubleshoot your NGINX configuration.
Check if your server is vulnerable.
Analyze your SSL/TLS configuration.